AI-discovered PHP vulnerabilities set off "Black October". Exploit discovery just stopped being the rate limiter
Critical vulnerabilities in PHP, found by teams using OpenAI and Google models, set off a cybersecurity alarm executives are calling "Black October," per the Guardian's report.
The decision it puts on your desk
Put a 24-hour patch SLA into your production stack this week, before the wave arrives. Add AI-origin findings to your threat model: systems budgeted against human-speed disclosures are mispriced now. And price your patch review for an October-November surge, because the executives named the season.
The security industry named itself a month on Friday, and the naming holds the useful warning.
AI-discovered critical vulnerabilities in PHP set off an alarm executives call "Black October," The Guardian reported, with warnings of an AI-enabled hacking "vulnerability tsunami."
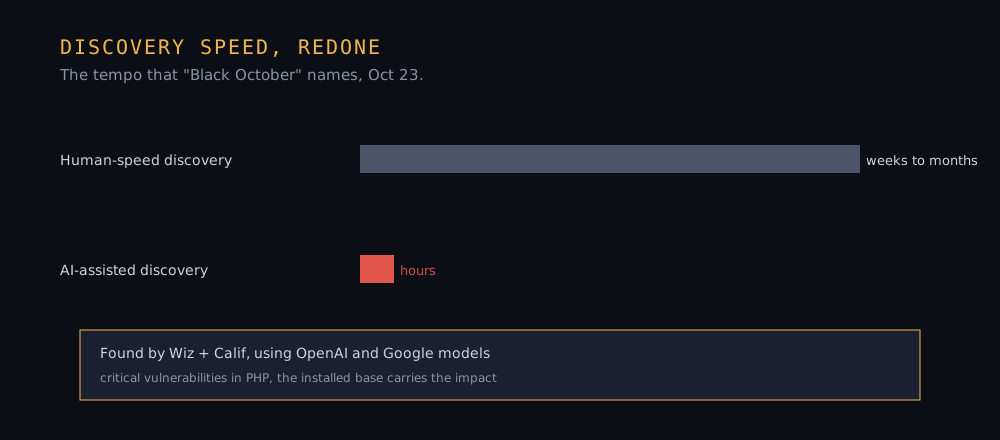
The discovery part came from Wiz and the AI firm Calif, using OpenAI and Google models to find the weaknesses, the reporting said.
The target carries the proof. PHP runs a large share of the web's server code, so critical weaknesses there land on an enormous installed base, and the discovery came from AI-assisted research rather than a human's multi-month hunt.
Careful framing, because the economics changed and the actor did not.
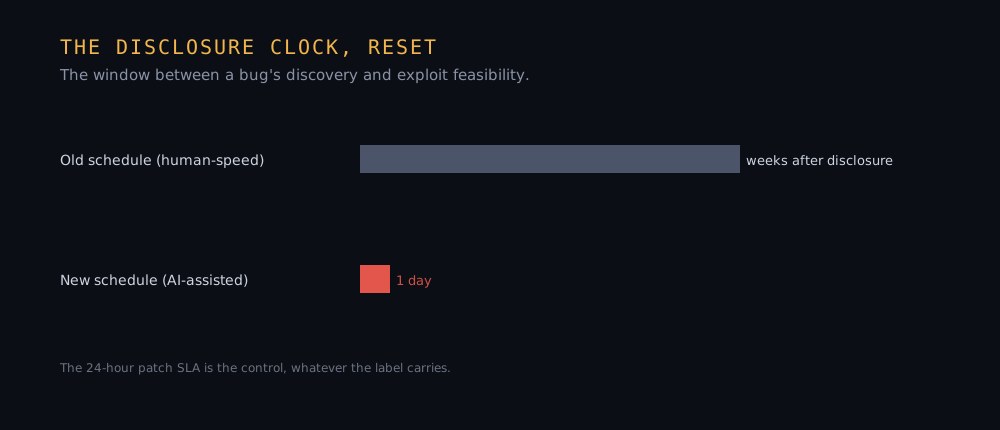
Nobody in the coverage disputes that attackers could find bugs before AI. The change sits in the rate: AI compresses discovery from weeks into hours, and the defense model that assumed weeks now carries a new schedule.
What the tempo does to patching
Follow the cost through the disclosure clock.
Vendors carry the visible line: every discovered critical bug now compresses the fixed window before an exploit appears.
Buyers carry the second cost. Patch windows that assumed weeks after disclosure now need a 24-hour standard, and the deadline applies to whatever production system cannot be repainted quickly.
Precedent in the legal frame: concern extends to disclosure itself, and security teams also cover the question whether AI research can still report bugs responsibly, since both discovery and exploitation books run at the same speed.
The unresolved edge is the real numbers. Without a published count of the wave, "Black October" rests on executive comments rather than a disclosed list, and the line to watch is where Google and Calif publish the findings.
I get the sense the defenses are already paid for. What changed is the innovation cycle; the fixes are on the calendar.
Source
← Previous
Meta's capex guide just broke the AI trade. The Nasdaq had its worst day in four months
Next →
Moonshot's Kimi K3.1 Pro lands fourth overall at a third of the price. The frontier gap is now three points
The Morning Recap
We sift the day. You make the calls.
The decision on every story, in your inbox before your first call.